Think like Sieged-sec?
Yet again, attackers surprise us
Yet again, attackers surprise us
Art is transient
As 2023 draws to a close, take control of what you read.
(no description available)
Recently, ransomware operators AlphV were in the news for telling the SEC that AlphV’s victim, MeridianLink, had not filed the relevant SEC form 8K about their breach. While this is something between clever, humorous and outrageous, I’d like to ask a question of those who advocate for adversarial thinking: Did you predict this?
A threat modeling conference, lots of government appsec guidance, and some updates from Shostack + Associates
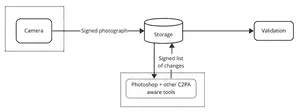
What can we learn from the C2PA security considerations document?
What can we learn from Gunnar Peterson’s Threat Model for Thanksgiving?
Exciting news from the SEC, lots of AI, and lots of threat modeling.
Principles are lovely, but do they lead us to actionable results?
Thinking about adversarial thinking
Best price ever for Threat Modeling
September was a big month in appsec for both memory safety and policy
The FDA has released their new guidance, which will be broadly impactful.
We can learn a lot from comparing retrospectives