Appsec roundup - July + August 2026
The CRA, how AI is showing up in security requirements, threat modeling, bug fixing and inventing biases in its spare time. Also, a lot of cool books by other authors.
The CRA, how AI is showing up in security requirements, threat modeling, bug fixing and inventing biases in its spare time. Also, a lot of cool books by other authors.
Join us in San Francisco for our popular 3-day Threat Modeling Intensive With AI
AI is disrupting software security, but traditional threat modeling remains the ultimate survival skill.
How can we shape a business strategy in an ‘AI world?’
The big takeaways from the OpenAI incident are over-reliance on benchmarks, anthropomorphization and volume.
Kymberlee on the Threat Modeling AI Systems community meetup at Black Hat
Our newest whitepaper introduces a new threat elicitation tool engineered specifically for LLMs.
From near misses to a new book on the C4 model and fundamental work by NIST showing the limits of today’s AI Guardrails, lots of exciting news about Application security.
Exploring what it means for an AI to explain itself, and why “it gave a reason” is not the same as accountability.
A busy Black Hat: A new talk, a new practical tool, and a deadline you should know about
LLMs are great at providing credible answers to questions. And those answers are worth looking at closely.
Exploring the fun in LLM threat modeling, and how it’s both an interface choice and a possibly ‘dark pattern’
Actionable lessons from delivering Threat Modeling Using LLMs, and using AI more generally.
This month kicks off with Donald Knuth being shocked by LLMs, then goes into the threat modeling impact of right to repair, and how to TM MCP, and a whole lot more!
This month's roundup starts with losing oneself, continues with cool new threat modeling tools and applications, and continues into appsec, AI and regulation.
The normalization of deviance, exciting threat modeling news, and a question of do regulatory threats change ‘the threat model’ as much as GPS attacks? Not yet.
Adam will be the featured speaker at the ISC2 Seattle Chapter meeting in February.
Read up on Adam's New Thing from October
Understanding ‘prompt engineering’
Everyone wants robots to help with threat models. How’s that working out?
Clarifying how to threat model AI
Podcast episode with Venkat Ramakrishnan discussing the intersection of GenAI and threat modeling
Exploring LLM-driven coding as I get ready for Archimedes
Solving hallucinations in legal briefs is playing on easy mode —— and still too hard
I haven’t done a lot of work in Python, and I’ve never used it to produce graphs. But after an hour of pair programming and then using Chatgpt and Github Copilot got me quite far in writing a set of Jupyter Notebooks, and dramatically shrunk the effort to use and debug a new tool. I wanted to record some thoughts on the experience, and what it means for programming and for application security.
Some inferences from layoffs in responsible AI teams
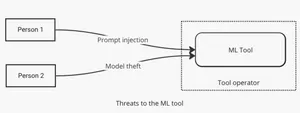
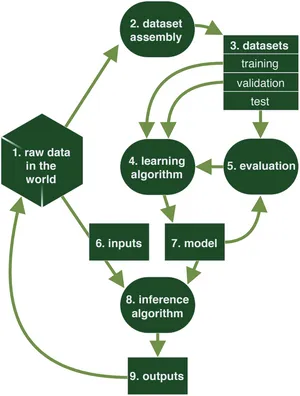
Some diagrams to help clarify machine learning threats
When will Adam Shostack be replaced by ChatGPT
ChatGPT in the headlines again
Risk Framework and Machine Learning
For my first blog post of 2020, I want to look at threat modeling machine learning systems.